

Top Kubernetes Security Tools for 2026
Key Takeaways Kubernetes security is a multi-faceted challenge encompassing admission control, network policy, runtime detection, and posture management. The market for Kubernetes security tools is...

Key Takeaways
- Kubernetes security is a multi-faceted challenge encompassing admission control, network policy, runtime detection, and posture management.
- The market for Kubernetes security tools is maturing, with both specialized vendors and broader Cloud-Native Application Protection Platforms (CNAPPs) offering robust solutions.
- Open-source projects like Kubescape, Calico, and Falco provide a highly competitive and production-ready foundation for many organizations.
- Effective Kubernetes security prioritizes preventing malicious workloads from deploying via admission control and segmenting internal pod-to-pod traffic to limit lateral movement.
- Organizations should evaluate solutions based on their existing infrastructure (e.g., OpenShift, AKS), development practices, and desired level of integration.
Securing Kubernetes environments is a complex undertaking, demanding a layered approach that addresses various stages of the application lifecycle and infrastructure. Effective Kubernetes security spans critical areas such as admission control, which gates what can be deployed; network policies, dictating traffic flow between pods; runtime detection, monitoring live workloads for anomalous behavior; and posture management, ensuring cluster configurations comply with security best practices across diverse multi-cloud architectures.
Table Of Content
- Key Takeaways
- The Decision Matrix: Choosing the Right Tool
- What Differentiates These Solutions
- Admission Control: The Critical Front Gate
- Network Policy: Containing Lateral Movement
- The Strength of Open Source
- The 10 Best Kubernetes Security Tools for 2026
- 1. Sysdig — best runtime and overall K8s depth
- 2. Aqua Security — best full lifecycle
- 3. Palo Alto (Prisma Cloud) — best platform breadth
- 4. Wiz — best context-first
- 5. Red Hat ACS (StackRox) — best for OpenShift
- 6. Snyk — best developer-first
- 7. ARMO (Kubescape) — best open-source posture
- 8. Tigera (Calico) — best network policy and eBPF
- 9. Microsoft Defender — best AKS economics
- 10. Uptycs — best unified telemetry
- Buyer’s Guide
As the Kubernetes landscape evolves, so does its security ecosystem. Specialized providers like Sysdig and Aqua Security are leading the charge, while Red Hat ACS offers tailored solutions for OpenShift deployments. Uniquely within cloud security, the Kubernetes domain boasts exceptionally strong open-source options, including Kubescape, Calico, and Falco. This analysis presents the top ten Kubernetes security tools for 2026, matched to common operational realities.
The Decision Matrix: Choosing the Right Tool
Selecting the optimal Kubernetes security tool hinges on an organization’s specific priorities and existing infrastructure. Whether the focus is on deep runtime analysis, full lifecycle protection, broad platform integration, or leveraging open-source capabilities, distinct solutions cater to different needs.
| If this describes you | Choose | Why |
| Runtime and K8s depth are priority | Sysdig — best runtime and overall K8s depth | Falco-lineage, deepest runtime |
| Full lifecycle, container-first | Aqua Security — best full lifecycle | Scan-assure-run with K8s assurance |
| Buying CNAPP breadth anyway | Palo Alto (Prisma Cloud) — best platform breadth | K8s on the platform graph |
| Context-first agentless | Wiz — best context-first | Graph correlation across clusters |
| OpenShift estate | Red Hat ACS (StackRox) — best for OpenShift | K8s-native, admission-strong |
| Developer-first shift-left | Snyk — best developer-first | Manifest/IaC scanning in CI |
| Open-source posture, want free | ARMO (Kubescape) — best open-source posture | CNCF posture, free core |
| Network policy and eBPF security | Tigera (Calico) — best network policy and eBPF | The K8s networking-security standard |
| Azure/AKS gravity | Microsoft Defender — best AKS economics | Included economics |
| Unified telemetry across estate | Uptycs — best unified telemetry | osquery/eBPF laptop-to-cluster |
Fundamentally, Kubernetes security aims to safeguard clusters across four key areas: admission control, which dictates what is permitted to deploy; network policies, governing pod-to-pod communication; runtime protection, monitoring live workload behavior and detecting deviations; and posture management, assessing cluster and Role-Based Access Control (RBAC) configurations. This protection also extends to the container images and Infrastructure-as-Code (IaC) templates that feed into the cluster.
What Differentiates These Solutions
Several core capabilities distinguish the leading Kubernetes security tools, each playing a crucial role in a robust defense strategy.
Admission Control: The Critical Front Gate
Admission control stands as the most impactful preventative measure in Kubernetes security. By intercepting and blocking unsigned, overly privileged, or vulnerable workloads before they are even instantiated, it proactively mitigates risks. This “shift-left” approach is inherently more cost-effective than responding to issues post-deployment. While most reputable tools offer admission control, their effectiveness varies in the sophistication of policies and the ease with which these policies can be defined and implemented.
Network Policy: Containing Lateral Movement
In its default configuration, Kubernetes networking is largely flat, allowing any pod to communicate with any other pod. This lack of segmentation creates a significant vulnerability, as a compromise in one pod can easily lead to lateral movement across the entire cluster. Tools leveraging Calico or eBPF-based policies, such as those derived from Cilium, transform this flat network into a least-privilege environment. This microsegmentation at the pod-to-pod level is essential for limiting the blast radius of a potential breach.
The Strength of Open Source
A notable characteristic of the Kubernetes security landscape is the genuine competitiveness of its open-source offerings. Kubescape — best open-source posture (a CNCF project), Tigera (Calico) — best network policy and eBPF (with an open core), and Falco (a CNCF runtime security project) are all production-grade and available for free. For many teams, these open-source solutions provide a baseline level of security that rivals commercial products, making them an attractive starting point.
The 10 Best Kubernetes Security Tools for 2026
1. Sysdig — best runtime and overall K8s depth
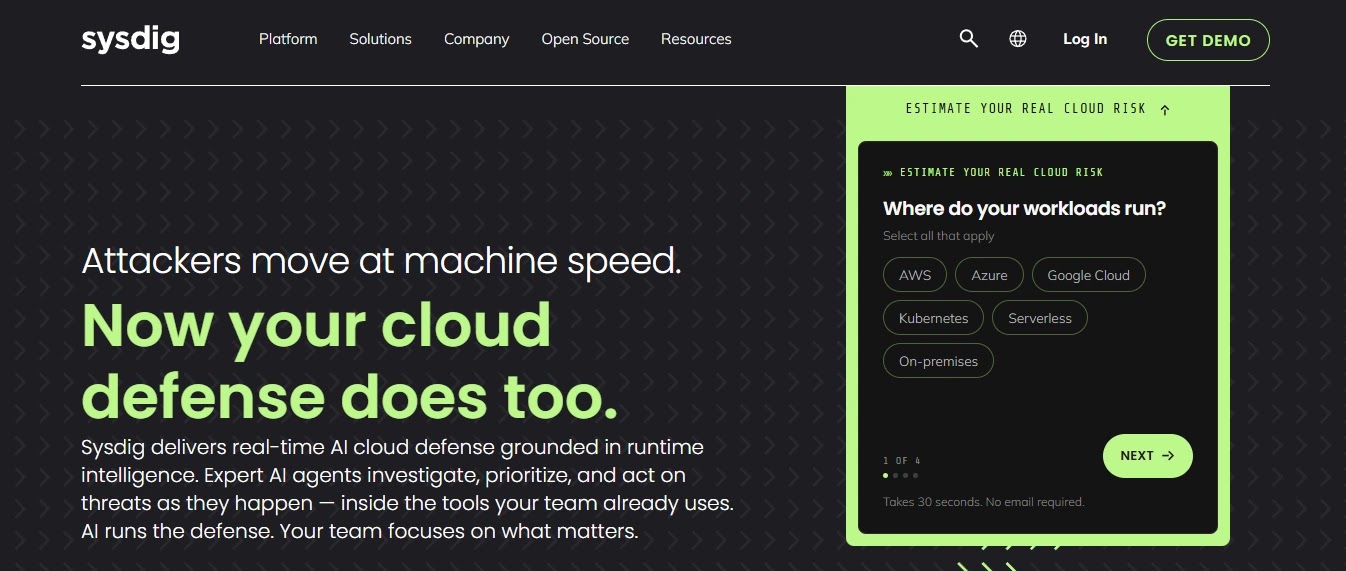
Sysdig serves as the commercial home for Falco, offering unparalleled depth in runtime detection. It provides robust drift control, advanced admission policies, and rich cloud context, purpose-built for Kubernetes. This platform delivers elite-level threat detection and behavioral analysis for live workloads.
- Wins: Exceptional runtime depth, Falco lineage, strong posture management and admission control.
- Strains: Broader VM/Windows coverage is not as extensive as some larger platforms.
2. Aqua Security — best full lifecycle
Aqua Security provides comprehensive “scan-assure-run” capabilities with potent Kubernetes assurance policies, admission control, and enforceable runtime protection. It also offers an open-source on-ramp via Trivy and Tracee for continuous container vulnerability scanning and broader cloud security.
- Wins: Deep lifecycle coverage, strong open-source integration, robust assurance policies.
- Strains: Breadth of coverage beyond cloud-native environments can be thinner.
3. Palo Alto (Prisma Cloud) — best platform breadth
Prisma Cloud integrates Kubernetes security seamlessly within its extensive Cloud-Native Application Protection Platform (CNAPP). It unifies admission control, runtime protection, and posture management under a single policy framework, alongside all other cloud security pillars.
- Wins: Comprehensive platform integration, strong performance across all Kubernetes security stages.
- Strains: Can involve complex credit modeling and a heavier user experience.
4. Wiz — best context-first

Wiz offers agentless cluster visibility, directly integrating with its cloud security and vulnerability graph. It correlates Kubernetes misconfigurations, workload vulnerabilities, and identity issues to identify actionable attack paths across multiple clusters.
- Wins: Powerful correlation capabilities, rapid multi-cluster visibility.
- Strains: Runtime sensor capabilities are relatively newer, and it comes at a premium price point.
5. Red Hat ACS (StackRox) — best for OpenShift
Red Hat ACS, built on StackRox technology, is a Kubernetes-native solution with robust admission control and policy-as-code capabilities. It is specifically engineered to mitigate risks such as privileged cluster paths and container privilege escalation across both OpenShift and upstream Kubernetes environments.
- Wins: Excellent Kubernetes-native integration, strong admission and configuration enforcement, deep OpenShift integration.
- Strains: Provides its deepest value within existing Red Hat ecosystems.
6. Snyk — best developer-first

Snyk emphasizes a developer-first approach, offering manifest, Helm, and Infrastructure-as-Code (IaC) scanning directly within IDEs and CI pipelines. It provides actionable, fix-first guidance, making it a highly adopted “shift-left” DevSecOps and code security testing layer.
- Wins: High developer adoption, clear fix guidance, strong configuration scanning.
- Strains: Not a runtime tool; requires pairing with other solutions for full coverage.
7. ARMO (Kubescape) — best open-source posture
Kubescape provides comprehensive, free, open-source posture management for Kubernetes. This CNCF project delivers robust compliance framework support and is easily adopted for assessing cluster configurations against security benchmarks.
- Wins: Free CNCF posture management, support for compliance frameworks, ease of adoption.
- Strains: Deeper runtime capabilities are typically available via commercial tiers; it is a relatively younger vendor.
8. Tigera (Calico) — best network policy and eBPF

Calico stands as the de-facto standard for Kubernetes networking and security. It leverages network policies and an eBPF dataplane to transform flat cluster networks into environments with least-privilege pod-to-pod control, aligning with Zero Trust network access principles.
- Wins: The industry standard for network policy, high eBPF performance, open-core model.
- Strains: Primarily focused on network and runtime; requires pairing with other tools for full posture and scanning.
9. Microsoft Defender — best AKS economics

Microsoft Defender for Containers/Cloud integrates Kubernetes posture management, admission control, and runtime protection. It offers favorable per-hour economics, multi-cloud extension via Azure Arc, and is backed by the broader Microsoft Defender cloud security suite.
- Wins: Cost-effective for Azure/AKS environments, seamless Defender integration, multi-cloud support through Arc.
- Strains: May not offer the same depth as specialized tools in certain areas.
10. Uptycs — best unified telemetry

Uptycs provides normalized osquery and eBPF telemetry across laptops, servers, and Kubernetes clusters. This unified data stream is invaluable for teams focused on comprehensive server security and workload hardening.
- Wins: Unified schema for telemetry, strong Kubernetes and Linux visibility.
- Strains: Product packaging and polish may trail some market leaders.
Buyer’s Guide
When approaching Kubernetes security, strategic implementation of controls is paramount. Prioritize prevention, segment your network, leverage open-source foundations, and meticulously guard your control plane.
- Enforce at Admission First: This is the most cost-effective and highest-leverage control. Implement policies to block privileged pods, require signed images, and deny deployments with critical vulnerabilities. Roll out these policies progressively.
- Segment Pod-to-Pod Traffic: A flat Kubernetes network allows a single compromised pod to access everything. Deploy Calico or eBPF-based network policies to achieve microsegmentation and enforce least privilege between pods.
- Utilize the Open-Source Foundation: Kubescape for posture, Calico for network policy, and Falco for runtime detection offer production-grade, free capabilities. Consider commercial platforms for enhanced management, correlation, and support as your scale demands.
- Protect the Control Plane and RBAC: Excessive cluster-admin privileges and exposed API servers represent critical risks. Posture tools that audit RBAC and control-plane configurations are essential for mitigating
Disclaimer: HackersRadar reports on cybersecurity threats and incidents for informational and awareness purposes only. We do not engage in hacking activities, data exfiltration, or the hosting or distribution of stolen or leaked information. All content is based on publicly available sources.






No Comment! Be the first one.