

ShinyHunters Exploits Critical Oracle PeopleSoft CVE-2024-21095 to Deploy Web Shells
Key Takeaways The ShinyHunters threat group is actively exploiting a critical vulnerability, CVE-2024-21095 (formerly CVE-2026-35273), in Oracle PeopleSoft systems. Attackers are bypassing Web...
Key Takeaways
- The ShinyHunters threat group is actively exploiting a critical vulnerability, CVE-2024-21095 (formerly CVE-2026-35273), in Oracle PeopleSoft systems.
- Attackers are bypassing Web Application Firewalls (WAFs) by employing a subtle character encoding technique in the request path.
- The campaign involves deploying web shells and memory-resident backdoors, including the SIDEEYE trojan, across a wide range of sectors.
- Affected organizations include those in technology, IT services, healthcare, agriculture, transport, and government, impacting systems containing sensitive HR, payroll, and operational data.
- Oracle has released a security patch for CVE-2024-21095, and immediate application is crucial for internet-facing PeopleSoft deployments.
The notorious ShinyHunters cybercrime group has launched a renewed wave of attacks targeting Oracle PeopleSoft systems, successfully circumventing Web Application Firewall (WAF) protections to install malicious web shells. This sophisticated campaign highlights a critical vulnerability, CVE-2024-21095 (previously identified as CVE-2026-35273), a severe flaw in PeopleSoft that was previously exploited as a zero-day against academic institutions.
Table Of Content
Security researchers at Google Cloud identified this latest mass exploitation effort and have attributed it to the group known as UNC6240, or ShinyHunters. The group’s ability to bypass established perimeter defenses by making minor modifications to attack requests underscores the persistent challenge of relying solely on WAFs without comprehensive software patching.
The current phase of attacks has broadened its scope beyond universities, now impacting organizations across diverse sectors, including technology, IT services, healthcare, agriculture, transportation, and government. These compromised PeopleSoft systems often house sensitive data such as human resources, payroll, and critical operational information, making them high-value targets for attackers.
According to a report from Google Cloud, ShinyHunters has successfully deployed web shells on dozens of systems globally. These web shells serve as initial access points, allowing the attackers to engage in direct, hands-on malicious activities within the compromised environments.
This evolving threat serves as a stark reminder that robust perimeter controls, while important, cannot fully substitute for timely software updates and patching. Previous incidents involving the same PeopleSoft zero-day remote code execution (RCE) vulnerability demonstrated how unauthenticated attackers could gain unauthorized access to exposed enterprise applications before a patch was made available.
ShinyHunters Bypasses WAF Protections
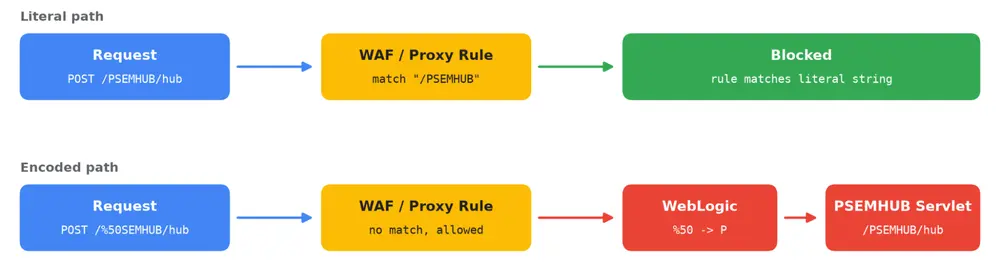
The effectiveness of ShinyHunters’ latest offensive stems from a clever WAF bypass technique. The attackers modified the vulnerable request path by encoding a single character instead of transmitting the standard endpoint name. Many WAFs and reverse proxies inspect incoming requests based on their literal string representation.
However, the Oracle PeopleSoft application server is designed to decode such requests before directing them to the intended service. This discrepancy allows the maliciously crafted, encoded request to slip past WAF rules that would otherwise block the unencoded version, ultimately reaching the vulnerable target. Detailed analysis of this bypass mechanism is available in a technical report.
Before proceeding with full exploitation, ShinyHunters typically sends multiple POST requests containing a serialized Java object. This reconnaissance phase allows them to confirm server vulnerability without necessarily writing files, making detection challenging. Even seemingly failed events in logs could indicate active reconnaissance, urging defenders to scrutinize logs across all nodes, especially in load-balanced environments.
Once a system’s vulnerability is confirmed, the attackers proceed to either establish persistent JSP-based web shells or execute commands directly in memory. The former provides a durable backdoor, while the latter can evade file-based security tools by leaving no new files on disk. This stealthy approach underscores the need for organizations to monitor both application and process activity comprehensively.
The current campaign also highlights a broader extortion risk. Past incidents, such as the Nissan PeopleSoft breach, have demonstrated the severe consequences of attackers gaining access to systems containing employee data. In the observed ShinyHunters activity, some commands were executed with root or SYSTEM-level privileges, and attackers gained access to PeopleSoft configuration and database connection details.
Web Shells Lead to Backdoors
On compromised Windows servers, the threat actors employed a secondary web shell to transfer a trojanized installer in segmented chunks, a technique used to circumvent request-size limitations. This installer then deployed the SIDEEYE backdoor into memory. SIDEEYE is a potent tool capable of stealing browser and desktop credentials, managing processes and files, and establishing interactive reverse shells or proxy connections.
Additionally, ShinyHunters utilized tunneling software to route internal network traffic through ordinary web connections. This allowed them to perform internal reconnaissance and move laterally beyond the initial PeopleSoft host. For Linux systems, remote-management tools were deployed to ensure persistence within the environment. This pattern necessitates a thorough investigation by security teams to determine if a PeopleSoft compromise has extended to connected databases or other internal servers. Even if the initial server is secured, a persistent foothold elsewhere could still lead to data exfiltration.
What You Should Do
- Apply Oracle Patch Immediately: Organizations must apply the Oracle security patch for CVE-2024-21095 without delay. Ensure all PeopleSoft deployments are running supported versions of PeopleTools.
- Disable or Remove Unnecessary Components: When not actively required, disable the Environment Management Hub. If feasible and appropriate, remove the affected application entirely.
- Review Access Logs: Scrutinize access logs for any instances of the encoded route (
/%50SEMHUB/) and associated external POST requests. - Inspect Web Application Directories: Conduct thorough inspections of PeopleSoft web application directories for any unauthorized JSP, JSPX, or executable files.
- Monitor Process Activity: Configure alerts for command shells spawned by the WebLogic Java process, as these can indicate in-memory exploitation.
- Incident Response Protocol: If a web shell or compromise is detected, treat it as a full system breach. Preserve forensic evidence, rotate all credentials associated with the application account, and monitor for unusually large outbound data transfers.
- Database Audit Review: Prepare for potential data theft and extortion by reviewing database audit logs for any bulk exports of sensitive HR, payroll, or student records.
Disclaimer: HackersRadar reports on cybersecurity threats and incidents for informational and awareness purposes only. We do not engage in hacking activities, data exfiltration, or the hosting or distribution of stolen or leaked information. All content is based on publicly available sources.







No Comment! Be the first one.